Privacy & Data Protection
Design and implement privacy programs that go beyond compliance checklists. We help you build privacy by design into your products and processes from the ground up.
We help organizations implement and mature Data Governance, Privacy, AI Governance, and Data Ethics programs—the foundation that makes Risk and Compliance manageable.
We're a specialist consultancy helping organizations design, implement, and mature their Data Governance, Privacy, AI Governance, and Data Ethics programs. Our consultants bring decades of hands-on experience building governance capabilities across global enterprises.
Whether you're starting from scratch or improving an existing program, we work alongside your teams to establish clear ownership, build sustainable processes, and develop the skills your organization needs to manage governance independently.
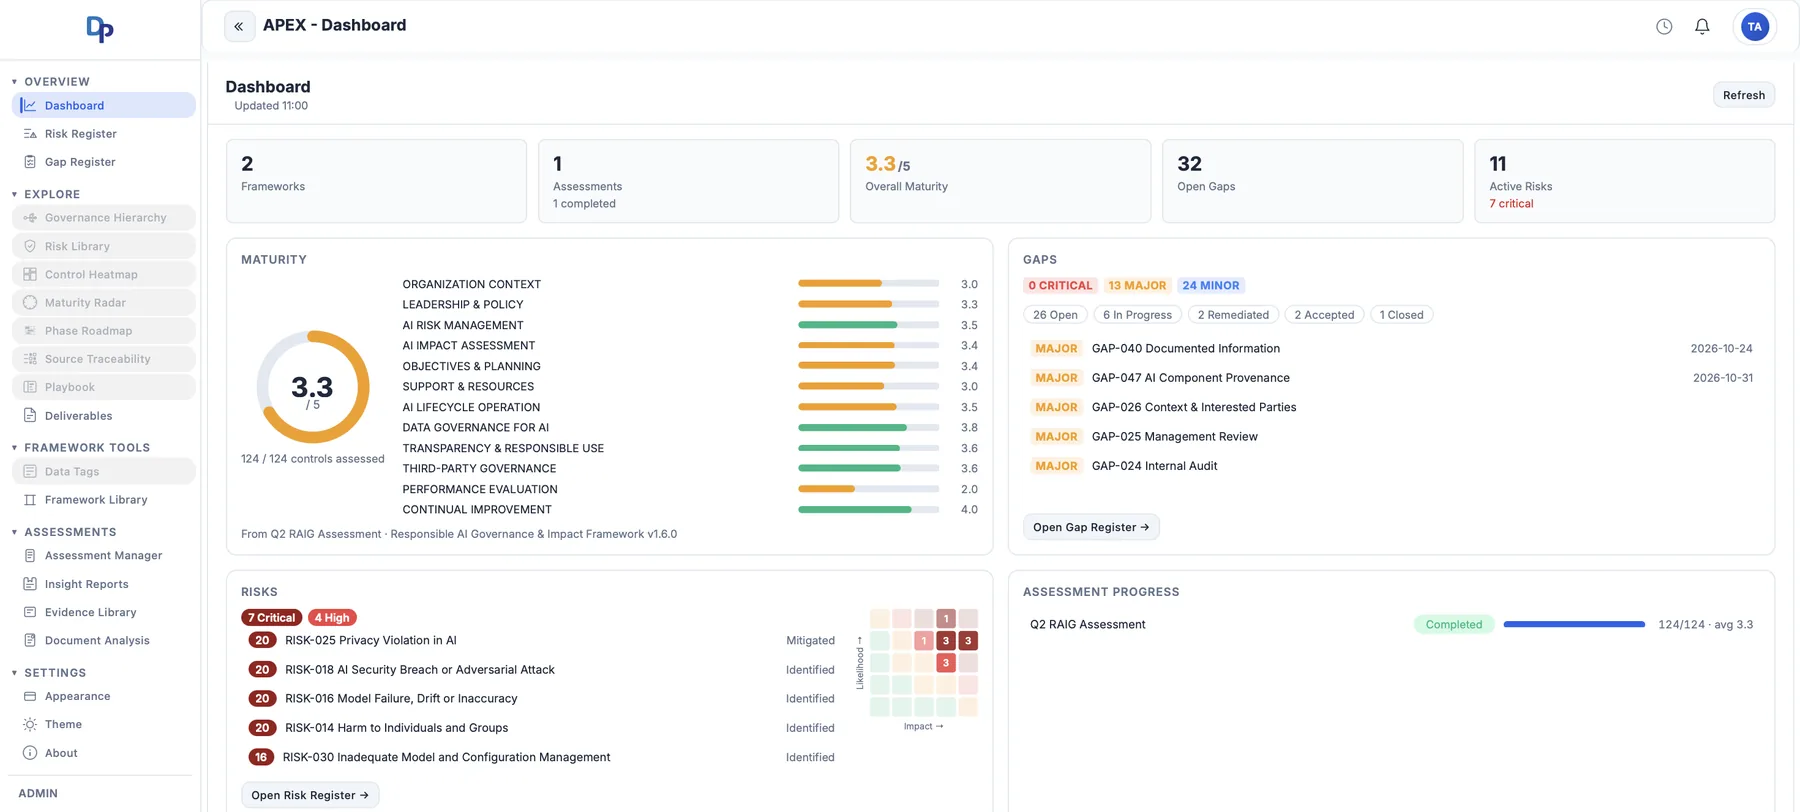
Our consulting work is supported by the APEX Governance Platform—a product we built and license to organizations running their own programs. APEX carries a governance program end to end: author the framework, assess maturity against your own evidence, track the gaps and risks that fall out, generate the policies and standards your controls call for, and report it all in a form an auditor will accept.
The bottom line: Risk and Compliance tell you what's wrong. Governance helps you get it right. We're the "G" that makes GRC actually work.
Consultancy: Hands-on guidance to design and implement governance programs tailored to your organization.
Frameworks: Proven, customizable frameworks so you can hit the ground running—not start from scratch.
Platform: APEX is licensed as a product—assessment, evidence, risk and gap tracking, deliverables, and reporting in one place.
We help you build and improve governance programs across the domains that matter most—creating the foundation your GRC tools need to deliver real value.
Design and implement privacy programs that go beyond compliance checklists. We help you build privacy by design into your products and processes from the ground up.
Establish robust governance frameworks with clear ownership, accountability, and stewardship. We help you build the capabilities to manage information as a strategic asset.
Build ethical decision-making into your data strategy. We help you create governance structures that ensure responsible use of data across your organization.
Implement governance frameworks for responsible AI. We help you build accountability, transparency, and oversight into your AI initiatives from development to deployment.
Govern the risk you inherit from others. We help you build vendor and third-party oversight—due diligence, contractual controls, and ongoing assurance—on the same structured foundation.
Building Data, AI, and Privacy governance programs where traditional GRC tools don't reach. While GRC tools help you prove compliance, APEX helps you build the governance programs worth proving—and then assesses them against your own evidence.
Principles → Capabilities → Requirements → Controls, anchored to a declared Primary Standard
Score controls against your own policies and reports, with an analyst approving every rating
Six-level maturity pathways and conformance status, tracked control by control
Everything a governance program needs between the framework on paper and the evidence an auditor asks for.
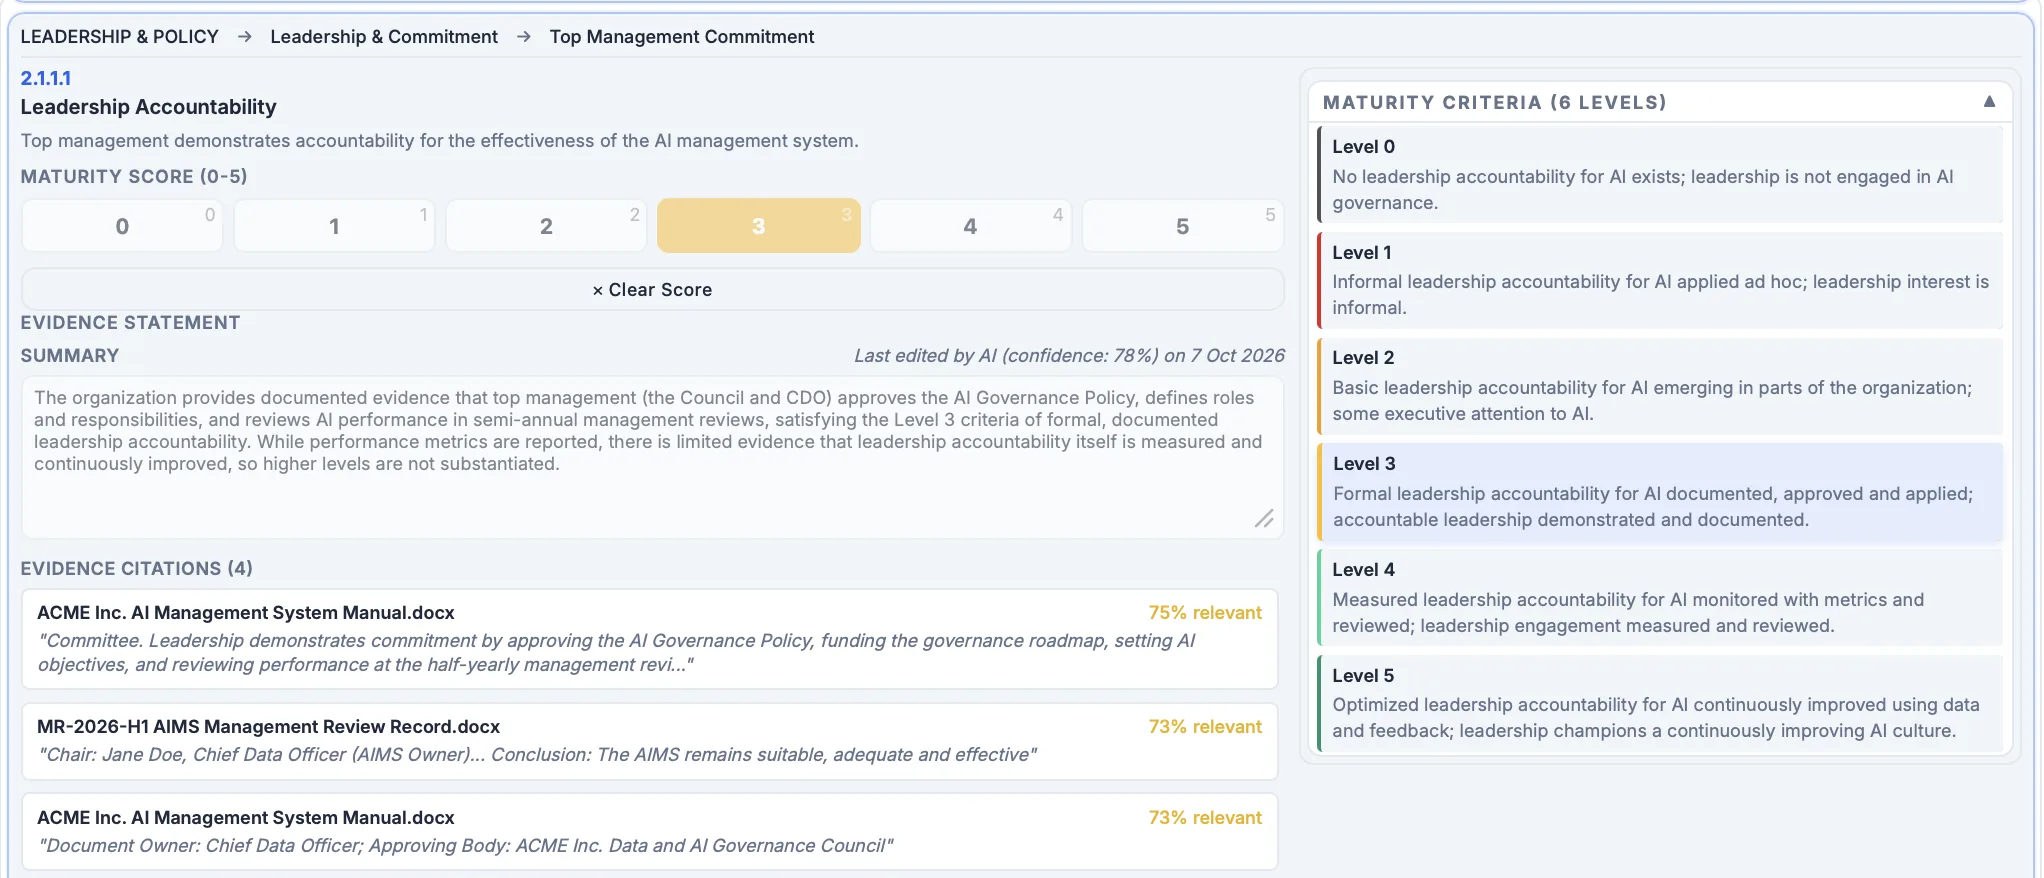
Upload policies, procedures, minutes and reports. APEX indexes them, finds the passages that speak to each control, and shows you exactly why a control got the evidence it did.
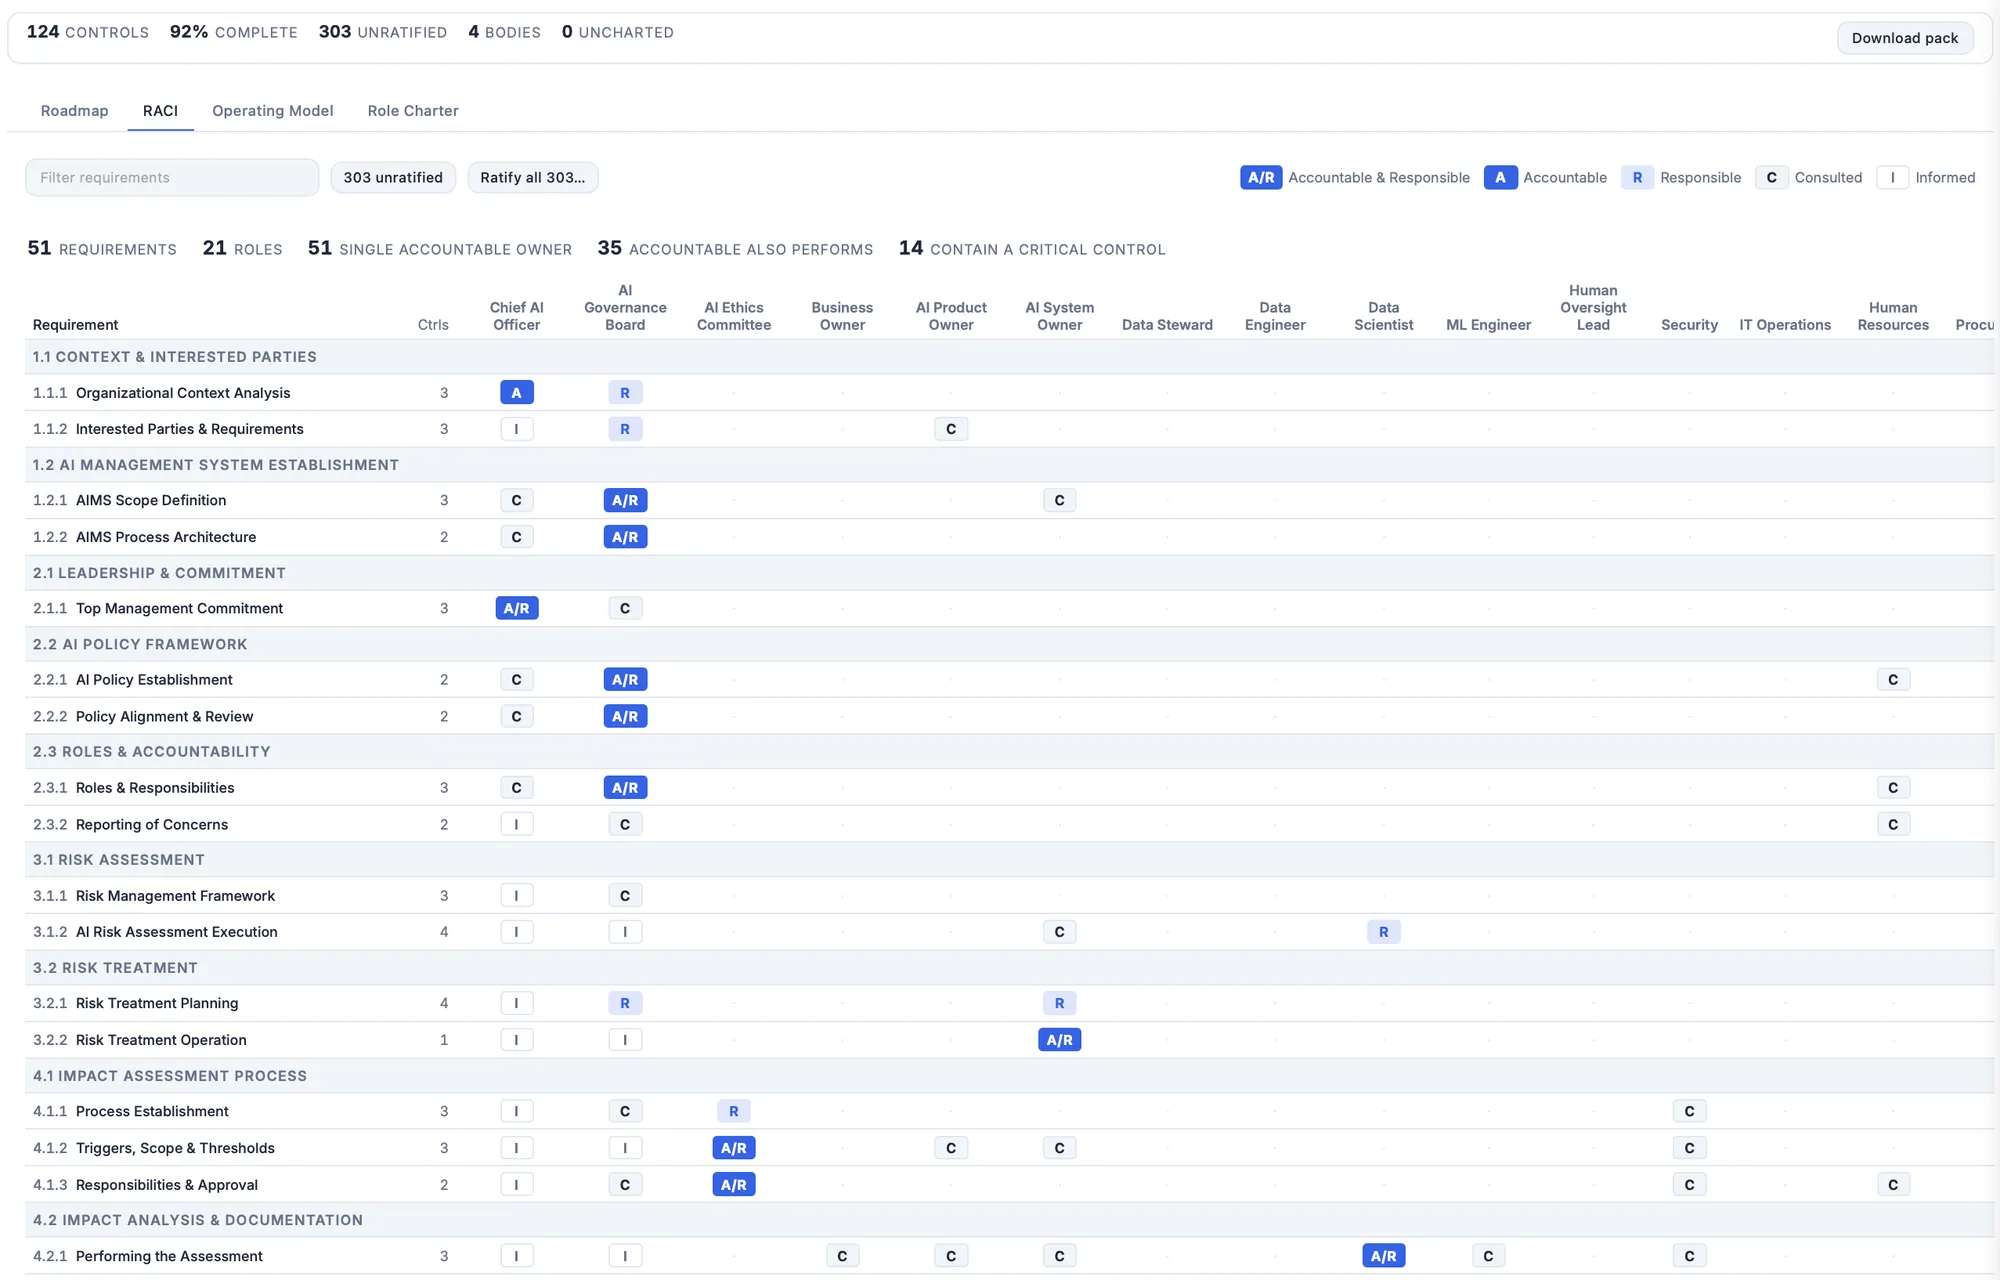
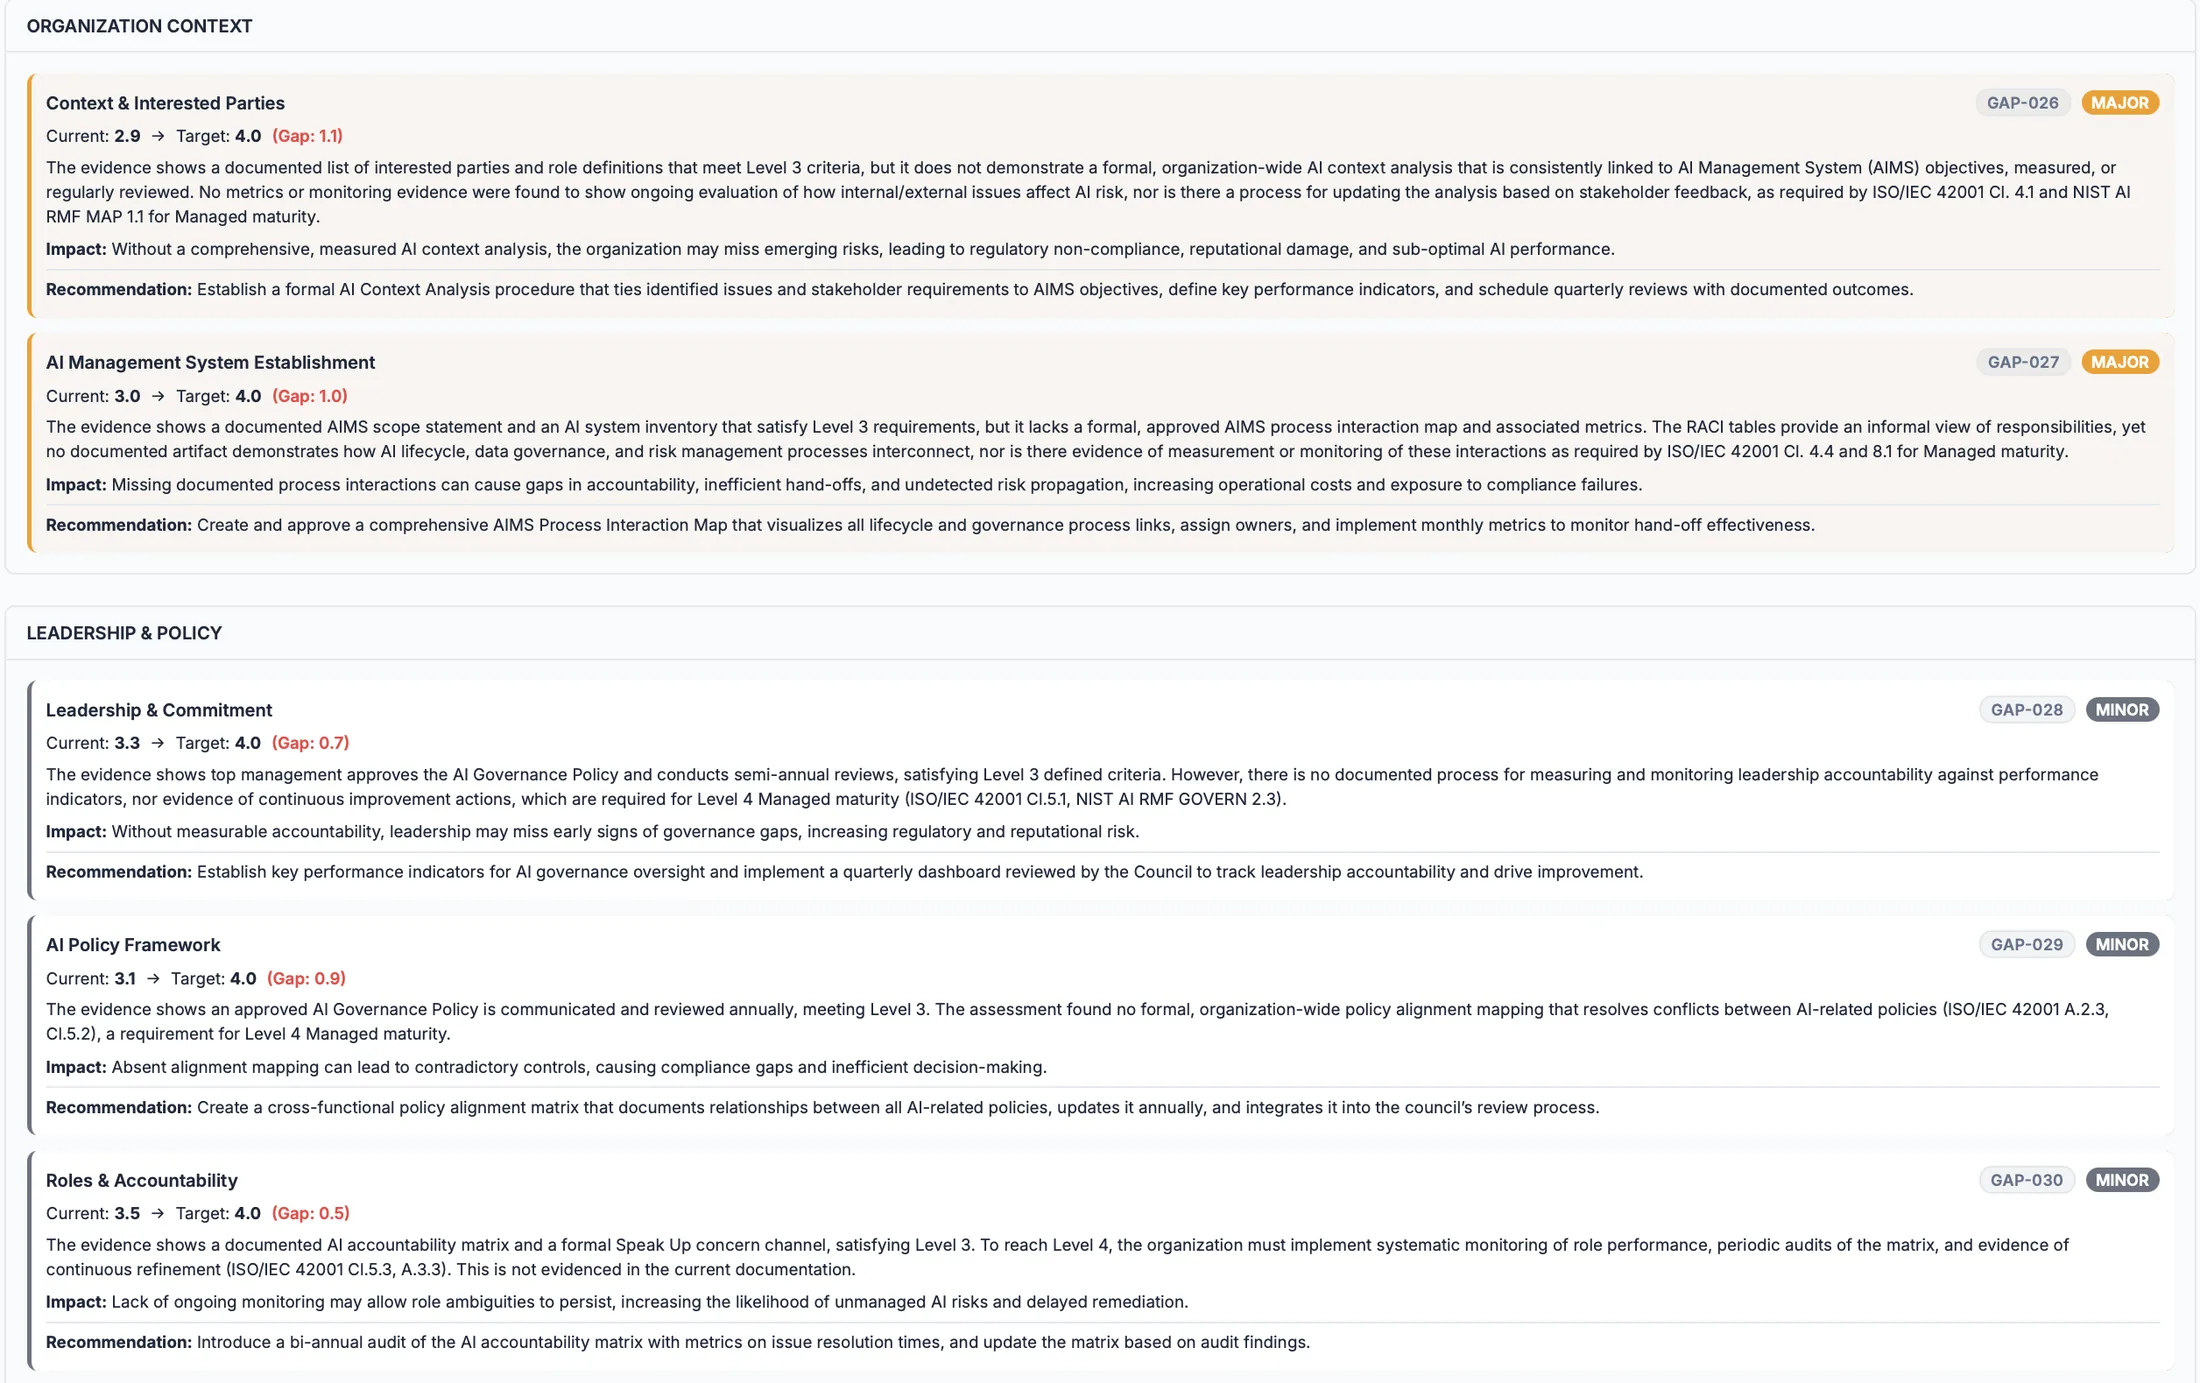
Frameworks ship with a Risk Library already mapped to controls. Assessment findings raise gaps, gaps link to risks, and both are tracked to closure with review flags and guided transitions.
Generate the policies, standards and charters your controls call for—dependency-aware, so a DLP standard cites the classification scheme it depends on rather than inventing its own. Exports to Word.
Maturity insight reports, assessment audit reports with the full retrieval trail behind every score, Statement of Applicability, and conformance exports. PDF, Word and Excel.
Governance hierarchy, maturity heatmap, radar and roadmap views—each drillable from principle down to individual control, with a dashboard summarizing the whole program.
Multi-tenant isolation, role-based access with per-framework grants, multi-factor authentication, append-only change history, and the option to bring your own language model.
A governance program is a loop, not a document. APEX runs the whole loop in one place.
Start from a ready framework or build your own, anchored to the standard you're accountable to.
Score maturity and conformance control by control, with proposals you review rather than accept blindly.
Ground every score in your own documents, with the source passage recorded against the control.
Findings become tracked gaps, linked to the risks they expose and the controls that mitigate them.
Generate the documents the gaps demand, sequence the work, and watch maturity move.
Produce the insight, conformance and audit reports your board, regulator or certifier expects.
A framework tells you what good looks like. The playbook tells you who does it, in what order, and how it's run. APEX generates the delivery layer from your framework, so your teams ratify it rather than write it from scratch.
25+ frameworks, each anchored to a named Primary Standard with full clause coverage. Comprehensive control libraries with implementation guidance, success metrics, maturity pathways and a bundled risk library—not just audit checklists.
Enterprise Data Management Capabilities
Data quality, stewardship, architecture, lifecycle management, and metadata governance.
Ethical & Effective AI Governance
AI ethics, bias detection, transparency, accountability, and risk management frameworks.
Multi-Jurisdictional Privacy Programs
Privacy by design, consent management, data subject rights, and cross-border compliance.
Vendor & Supply Chain Governance
Due diligence, contractual controls, ongoing monitoring, and exit management for the risk you inherit from vendors.
Comprehensive Integrated Framework
The Data, AI and Privacy frameworks combined into a single integrated governance program for holistic digital governance.
Standalone Frameworks Available: ISO/IEC 42001, ISO/IEC 27701, ISO 38505, EU AI Act, NIST AI RMF, NIST Privacy Framework, OECD AI Principles, GDPR, CCPA, HIPAA, PCI-DSS 4.0, SOC 2, BCBS 239, COBIT 2019, TOGAF 10, Privacy by Design, PIPEDA (Canada), Saudi PDPL, and more.
Regional & National Standards: Qatar National Data Policy and National Data Standards (NPC P001 / S001), QCB Data Handling & Protection Regulation, and the Qatar Personal Data Privacy Protection Law (PDPPL)—each built out as a full framework, not a mapping exercise.
Tailored to your sector and jurisdiction. The governance core is common, but the edges aren't—banking supervision, health regulation, data localisation and cross-border rules all shape the controls you actually need. We build to your industry and the laws you answer to.
Interactive visualizations and assessment tools that transform governance frameworks into actionable insights.
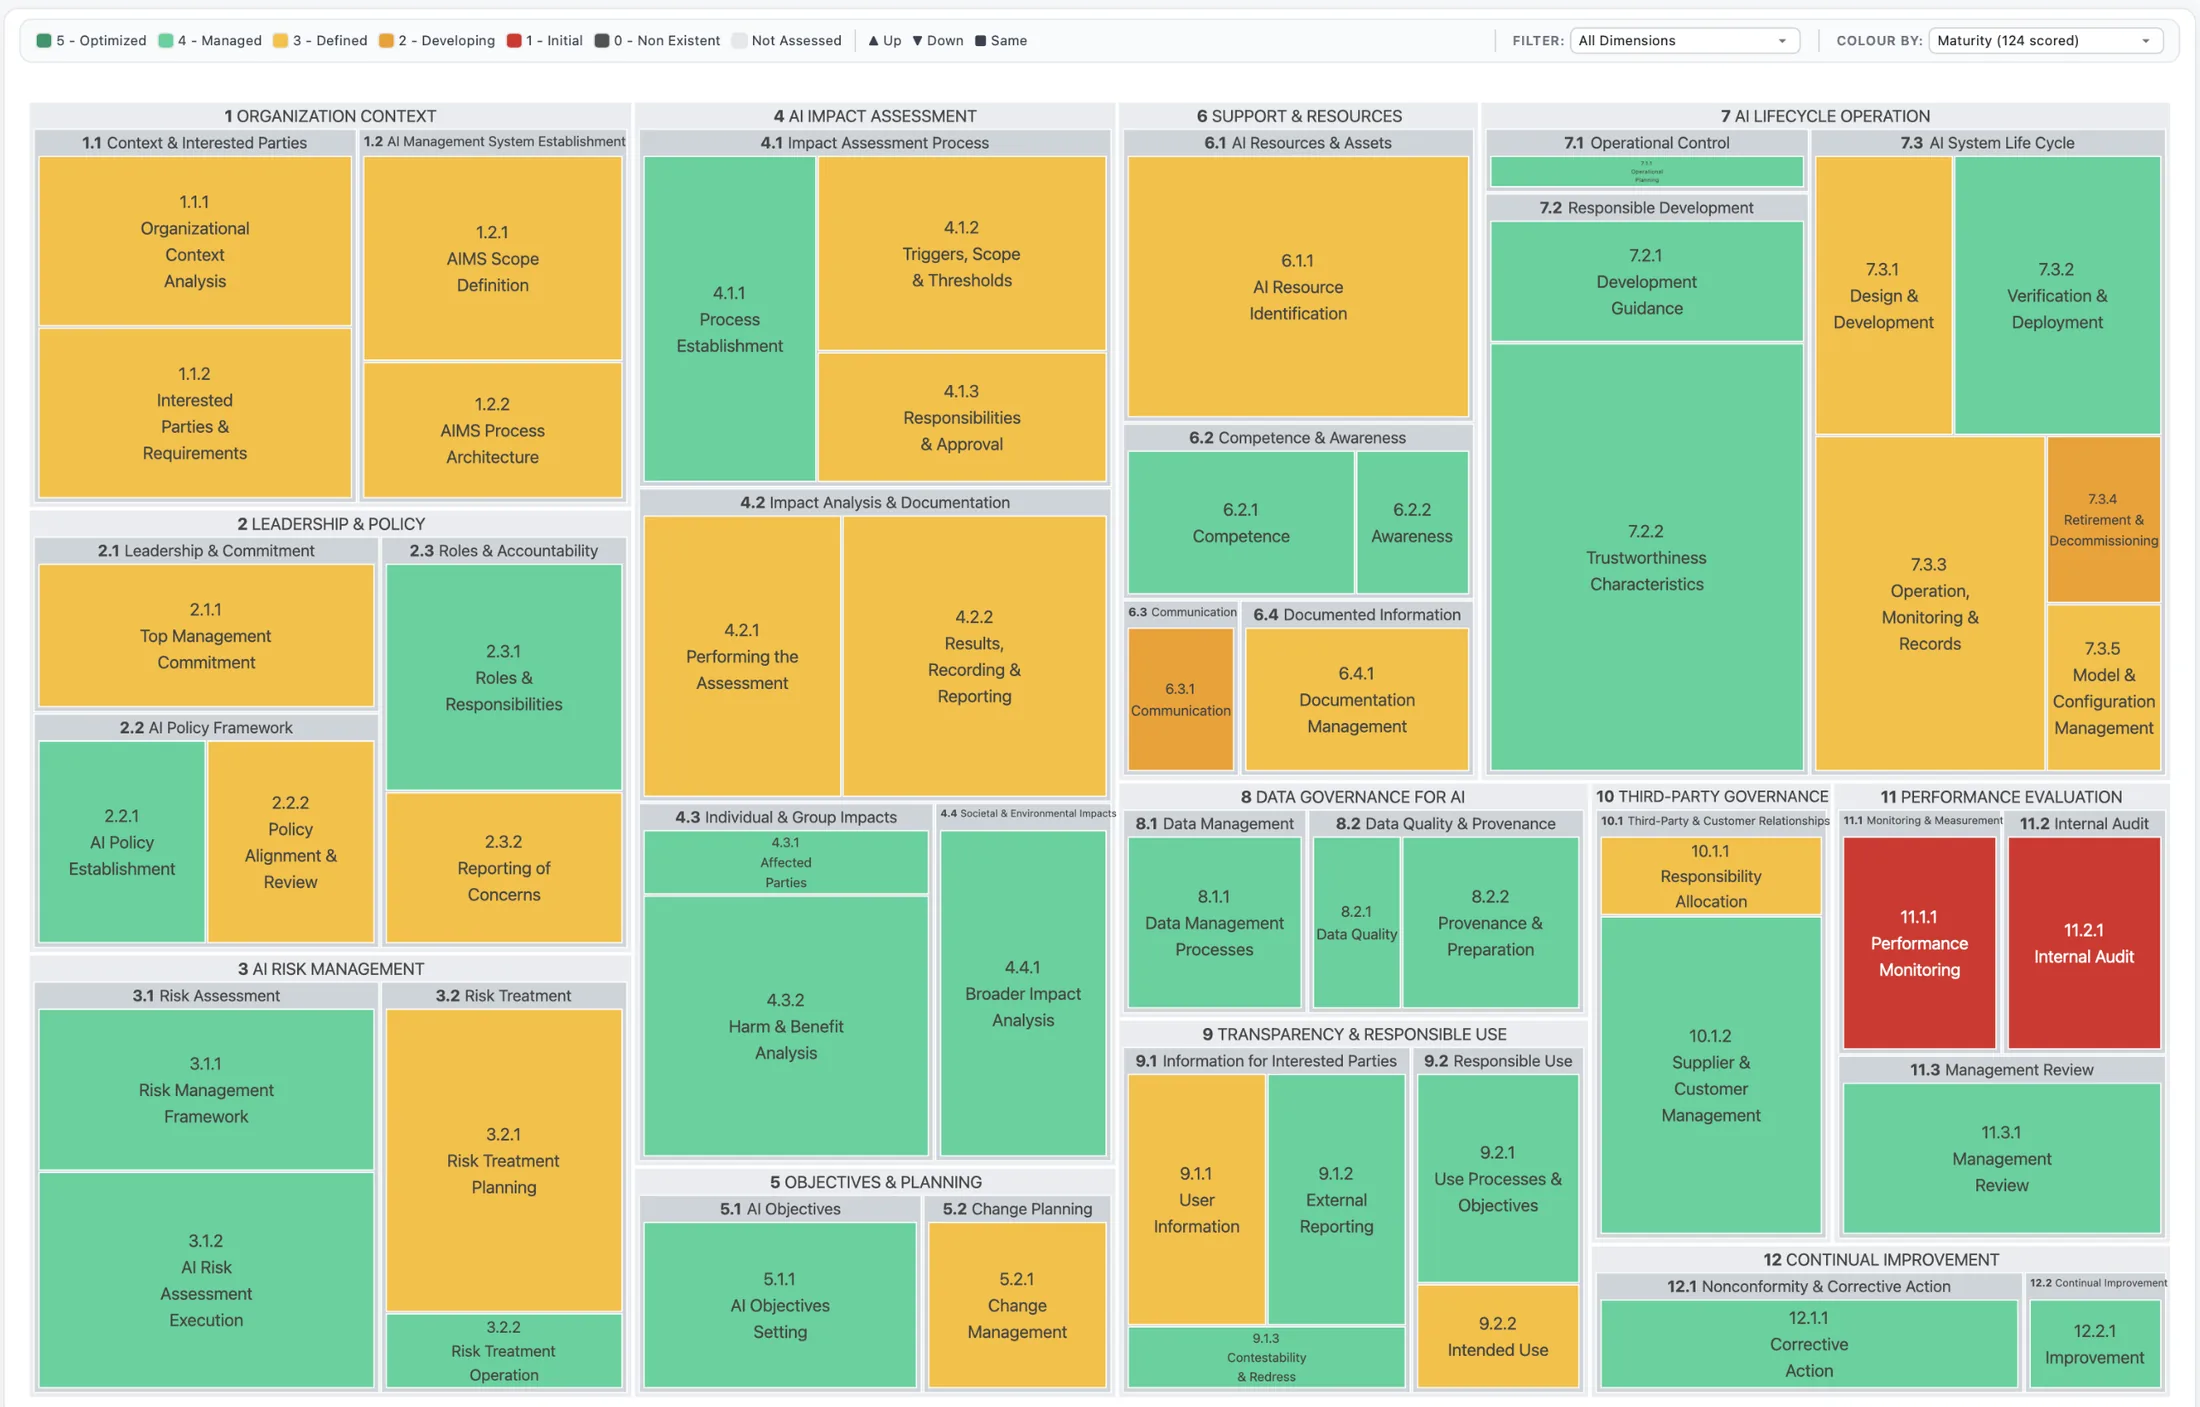
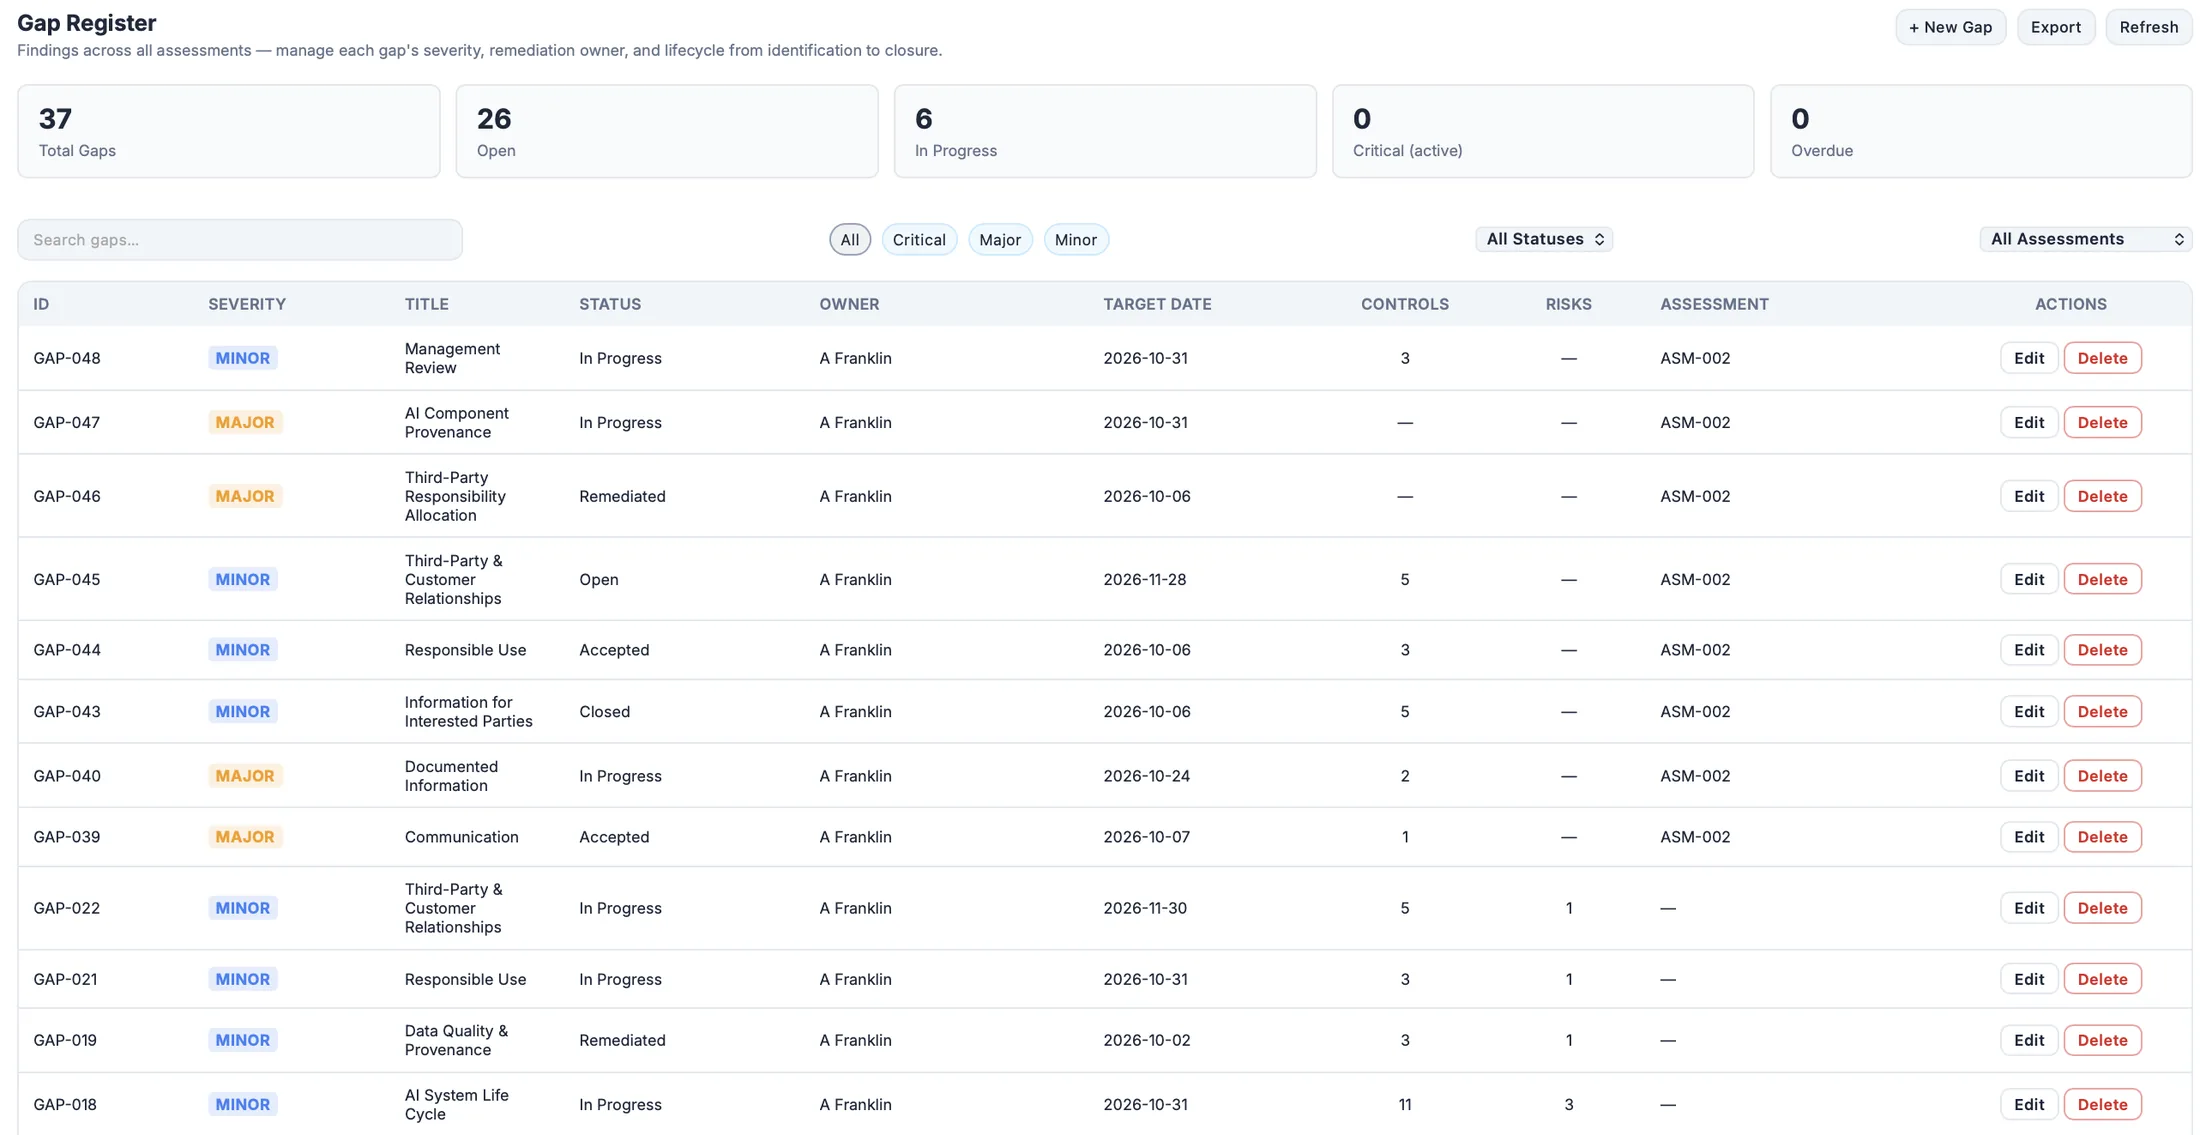
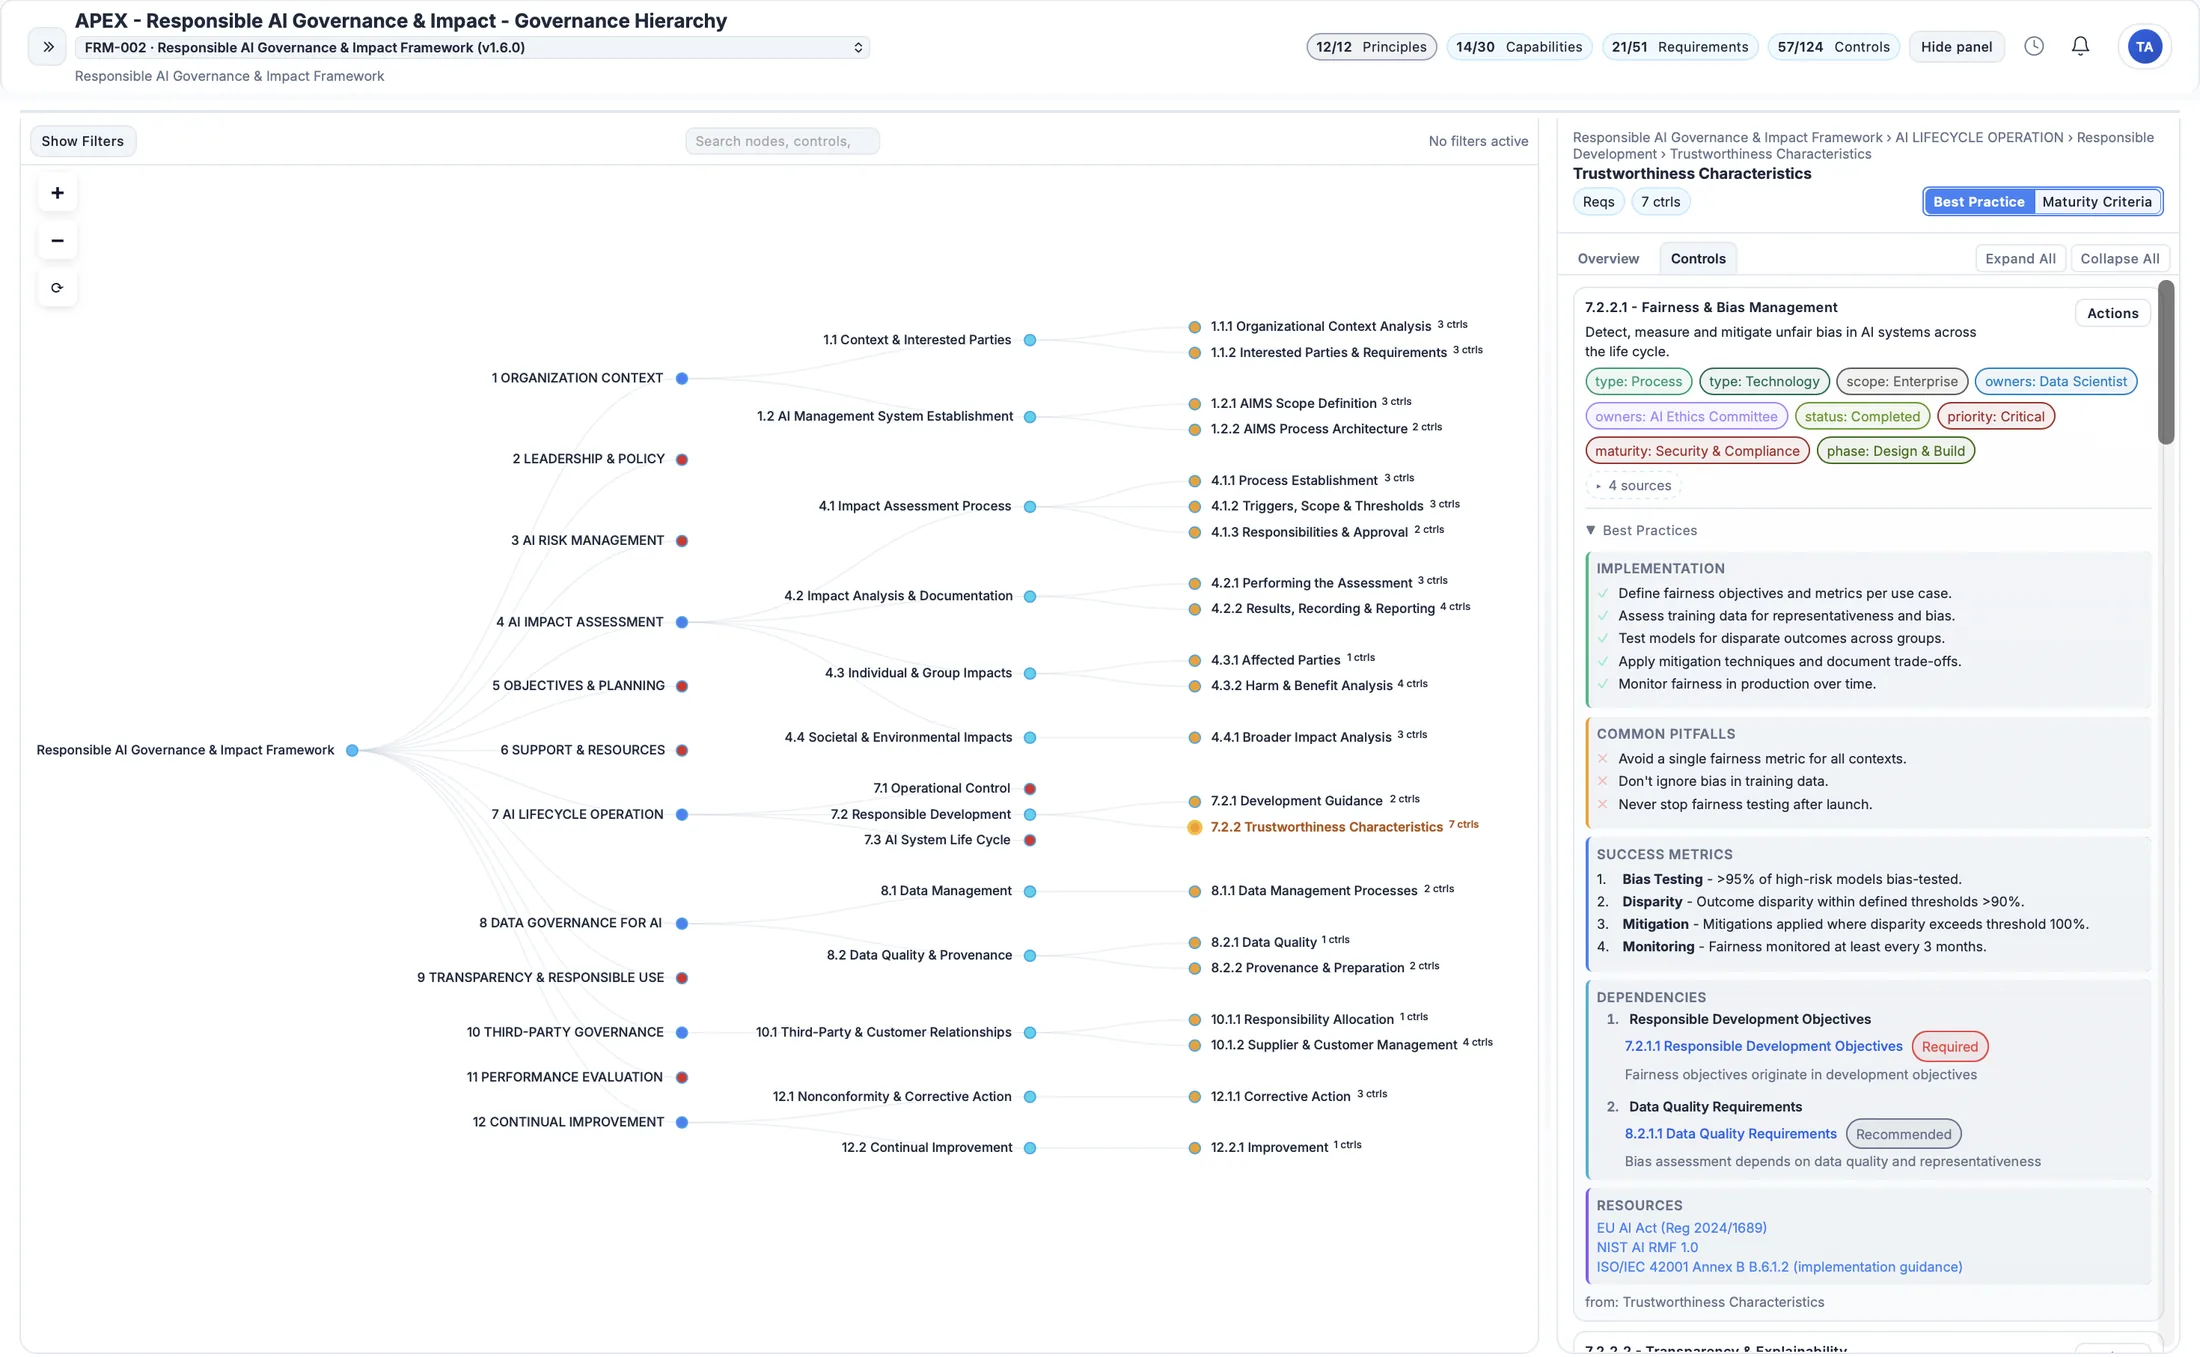
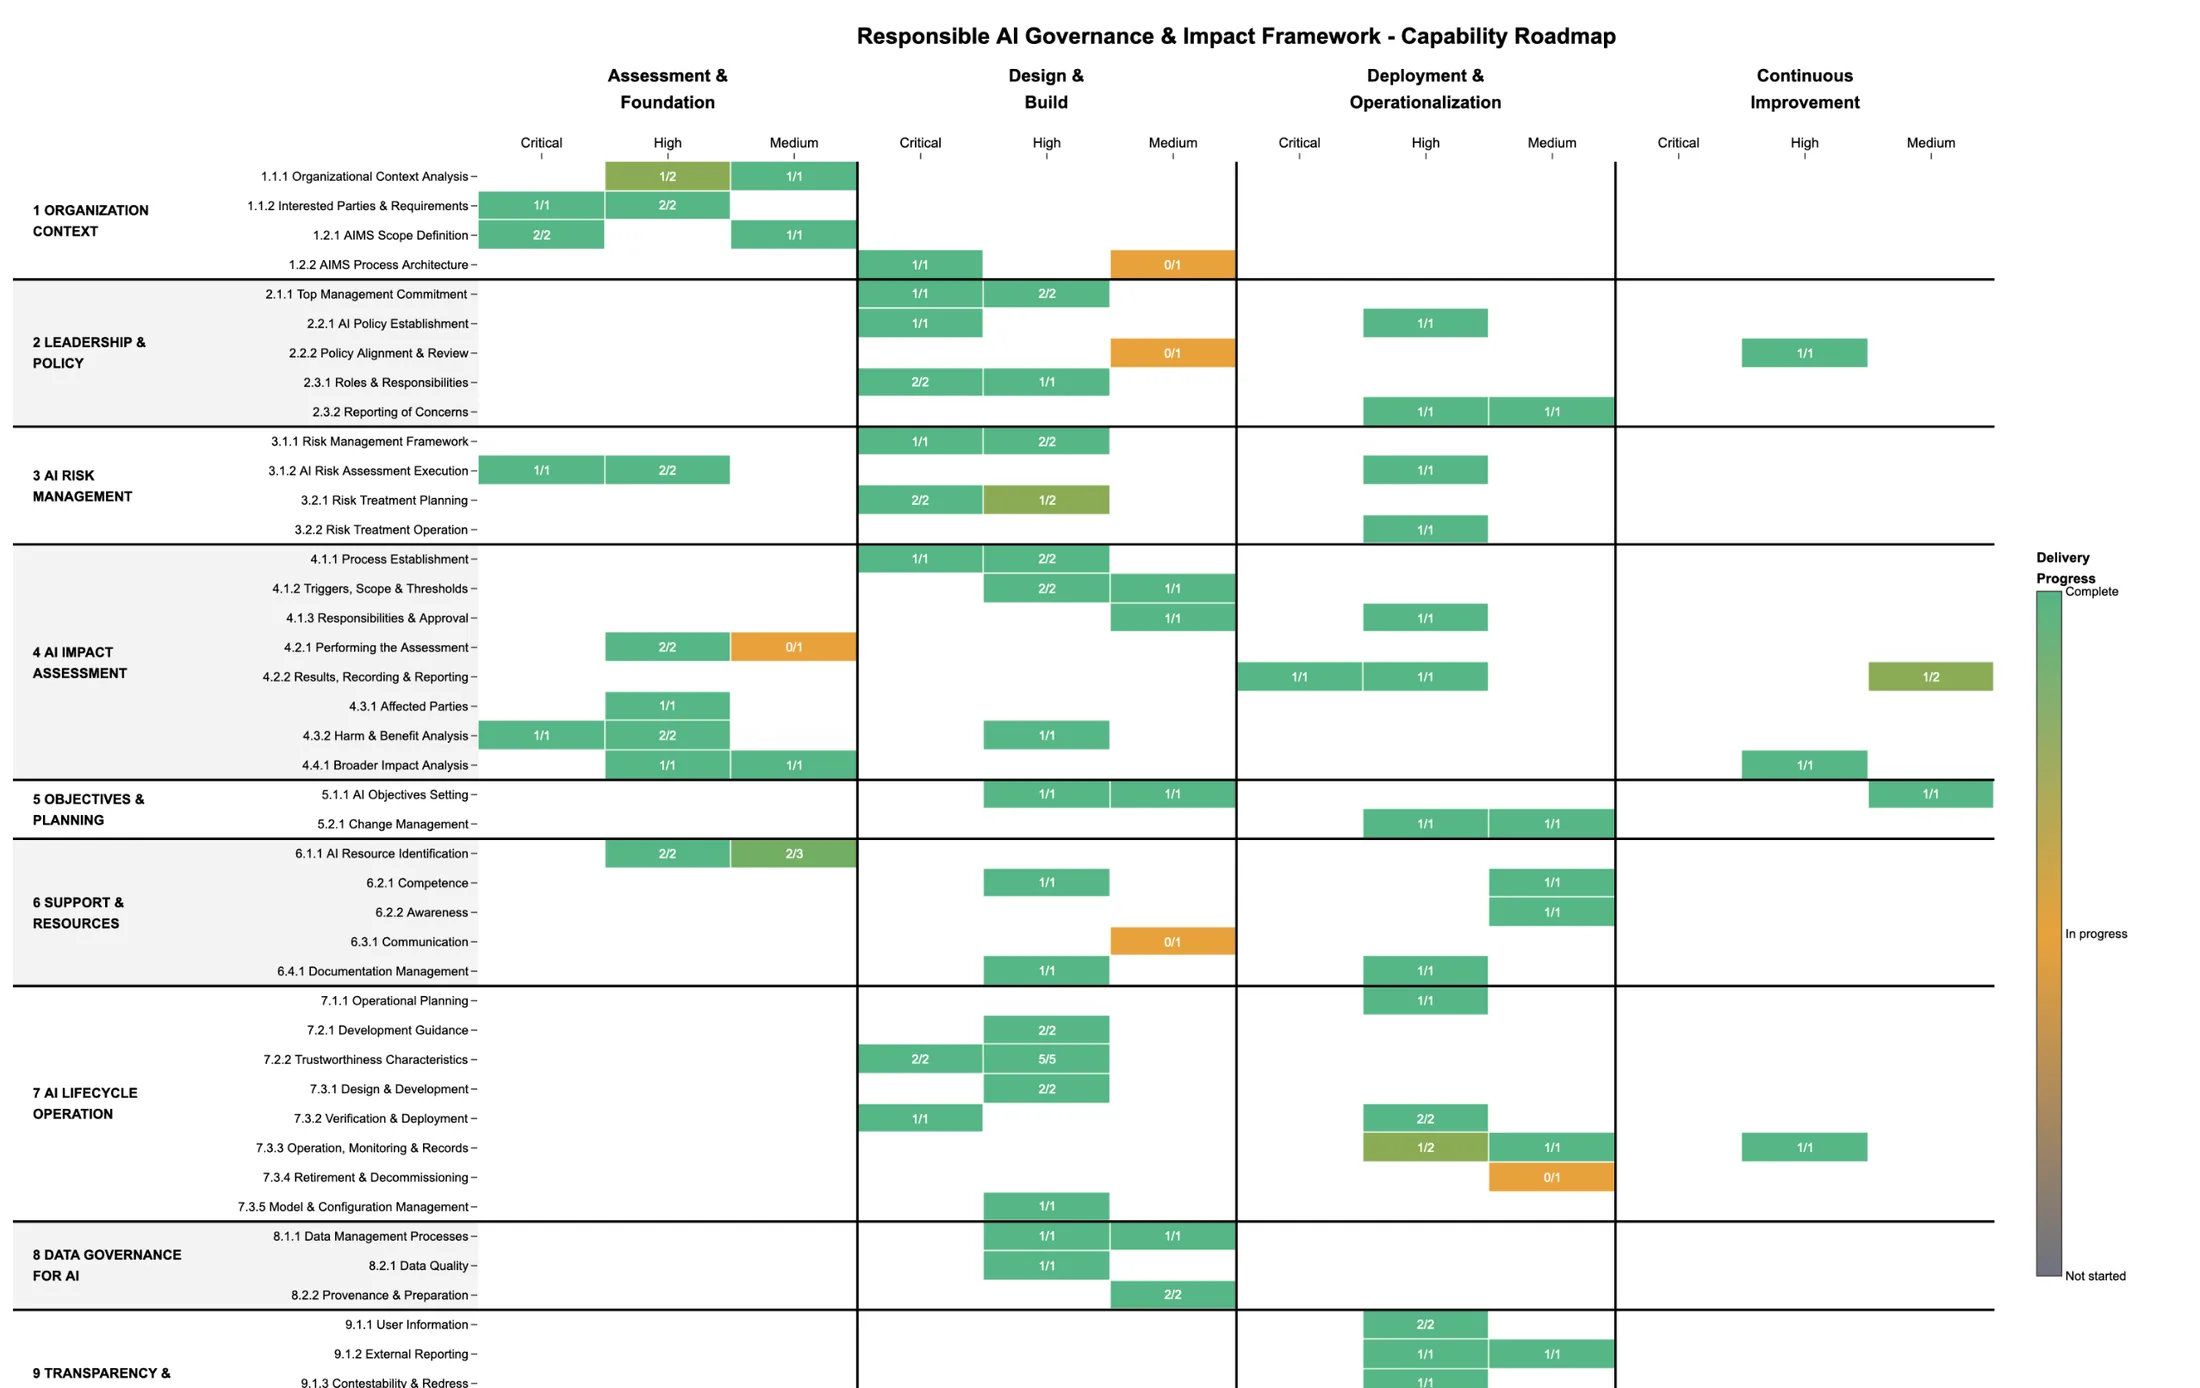
GRC tools help you track compliance. We help you build the governance programs that make compliance achievable in the first place. Here's what sets us apart.
Our consultants bring 25+ years of hands-on governance experience across global enterprises including major airlines, retailers, and telecommunications companies. We've seen what works—and what doesn't.
Every framework declares one Primary Standard and covers 100% of its clauses, with named Secondary standards cited only where they genuinely add something. No vague "aligned to ISO"—you can check our coverage against the standard itself.
APEX isn't a house style—it's a documented, versioned standard with a changelog and a validator that enforces it. Principles, Capabilities, Requirements, Controls; every control carrying implementation steps, pitfalls, measurable success metrics and six levels of maturity criteria.
We don't just assess and leave. We work alongside your teams to build sustainable governance capabilities—practical guidance, clear roadmaps, and hands-on support until you're self-sufficient.
The same standard can produce a framework shaped to pass a certification, or one shaped to run a program day to day. We decide which at the start, deliberately—rather than discovering later that the framework fits the wrong job.
Statements of Applicability, conformance exports, gap registers, and audit reports that show the evidence behind every score. It drops into your GRC tooling, and it stands up on its own when someone asks how you know.
You're putting your policies, assessments and gaps into APEX. Here's how it's protected.
Email one-time-passcode MFA, enforced password rotation on provisioned accounts, and rate-limited sign-in.
Role-based permissions down to the individual capability, plus per-user grants controlling which frameworks each person can even see.
Every organization's frameworks, evidence, assessments and reports are scoped to its own tenant and never cross over.
Assessments, scores and gaps carry a change history that can be added to but never rewritten. Completed assessments lock; only an admin can reopen one.
Personal data is redacted as evidence documents are ingested, so the sensitive detail in your source material doesn't propagate through analysis.
Point APEX at your own language model and embedding provider, with per-tenant token caps and usage tracking. Your evidence goes where you decide.
Whether you're licensing APEX for your own team, engaging us to build the program, or both—let's talk about where you are and what you need next.